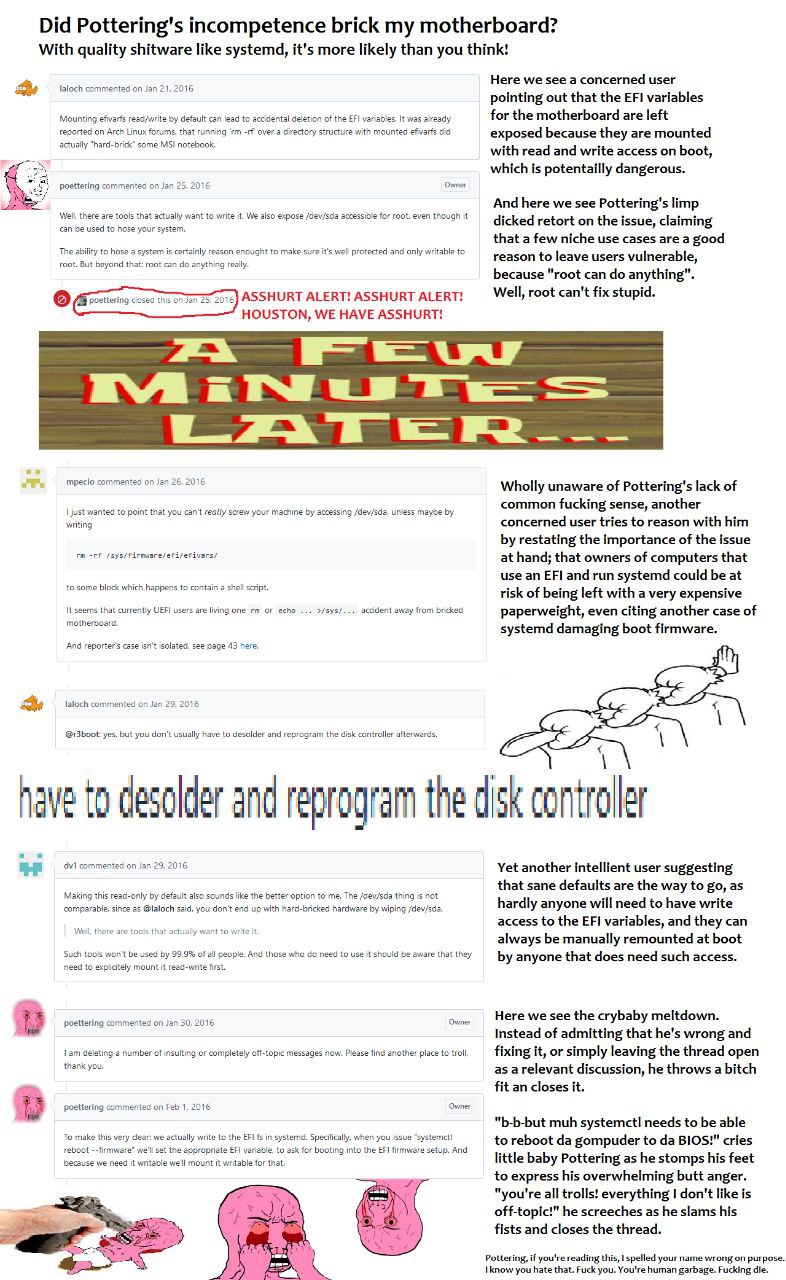
Did Pottering's incompetence brick my motherboard? With quality shitware like systemd, it's more likely than you think! faloch commented on Jan 21. 2016 Here we see a concerned user pointing out that
2026-09-27 02:29
telegramthe_high_council_of_frens
OCR
Текст, распознанный с картинки.
Did Pottering's incompetence brick my motherboard?
With quality shitware like systemd, it's more likely than you think!
faloch commented on Jan 21. 2016
Here we see a concerned user
pointing out that the EFI variables
Mounting efivarts default can jead to deletion of the vanabies. It was aveady
for the motherboard are left
on Arch Linux forums. that
ning over a directory structure with mounted efvarts cid
exposed because they are mounted
actuslly some notebook,
with read and write access on boot,
which is potentailly dangerous.
poettering comment:
And here we see Pottering's limp
Well, there are tools that actually want to write We also expose /dev/sda for root. even though it
dicked retort on the issue, claiming
can used to hose your system,
that a few niche use cases are a good
The abili
ity to hose a system is
ort
to make
well protected and only writable to
root.
beyond that: root can anything really.
reason to leave users vulnerable,
because "root can anything”.
ASSHURT ALERT! ASSHURT ALERT!
Well, root can't fix stupid.
HOUSTON, WE HAVE ASSHURT!
commented on Jan 26. 2016
Wholly unaware of Pottering's lack of
common fucking sense, another
jus
aNted to point that you can't really screw your machine accessing unless mayoe
writing
concerned user tries to reason with him
restating the importance of the issue
at hand; that owners of computers that
use an EFI and run systemd could be at
to some blode which happens to contain
nol script.
risk of being left with a very expensive
It seems that users are living one or echo
away from bricked
paperweight, even citing another case of
systemd damaging boot firmware.
And reporter's case isn't see page 43 here,
on
yes. but you don't usually have to desolder and rep
controller afterwards.
nave to desolder and reprogram the disk controler
a
commented on Jan 29, 2016
Yet another intellient user suggesting
Making this read-only default also sounds like the better option to me, The /cev/sda thing
that sane defaults are the way to as
hardly anyone will need to have write
comparable, since @laloch said, you don't end up with hard-bricked hardware wiping
to
access to the EFI variables, and they can
We
act
always be manually remounted at boot
Such too’s won't be used 99.9%
opie. And those whe need to use it should be that they
anyone that does need such access.
need 10 mount it
poettering commented on Jan 30, 2016
Here we see the crybaby meltdown.
Instead of admitting that he's wrong and
deleting а number of insulting or completely off-topic messages now. Please find enother place to troll
fixing it, or simply leaving the thread open
thank you
as discussion, he throws a bitch
fit an closes it.
commented on Feb 1, 2016
Owner
"b-b-but muh systemctl needs to be able
actually write to the
sternd. Specifically, when you
dea
to reboot gompuder to BIOS!" cries
the
for booting into the EFI firmware setup, And
use Wwe Need it well mount it writable for that.
little baby Pottering as he stomps his feet
to express his overwhelming butt anger.
"you're all trolls! everything don't like is
off-topic!" he screeches as he slams his
fists and closes the thread.
Pottering, if you're reading this, your name wrong on purpose.
know you hate that. Fuck you. You're human garbage. Fucking die.
lang: ru+en
Пользовательские термины
Свои поисковые фразы (до 280 символов). При поиске по термину счётчик растёт.
Пока нет пользовательских терминов.