CVE-2018-90017117 Also known as: #KingMe attack Published 2018-12-03 Common Vulnerabilities and Exposures Partial embargo until 2019-04-01 Reported of East Coast Hacking Organization Description An in
2026-09-26 22:24
telegramthe_high_council_of_frens
OCR
Текст, распознанный с картинки.
CVE-2018-90017117
Also known as: #KingMe attack
Published 2018-12-03
Common Vulnerabilities and Exposures
Partial embargo until 2019-04-01
Reported of East Coast Hacking Organization
Description
An input validation error in the move parser allows remote privilege escalation.
Background
The popular internet chess site lichess.org allows for the import of PGN files, a standard text-based inter-
change format for giving the sequence of moves in a game. Moves look like (move a pawn to the
square) or “Qxd3” (queen captures on or “Рсс8" (the rook on the С file moves to When a pawn
moves into the last or first rank, it usually promotes to queen, but may legally promote to a bishop, knight,
or rook at the player’s option. This preference is specified using the notation (or for knight, for
rook, or for queen to optionally be explicit). lichess.org does
not properly implement this syntax, and allows a move like
which is not legal chess.
Impact
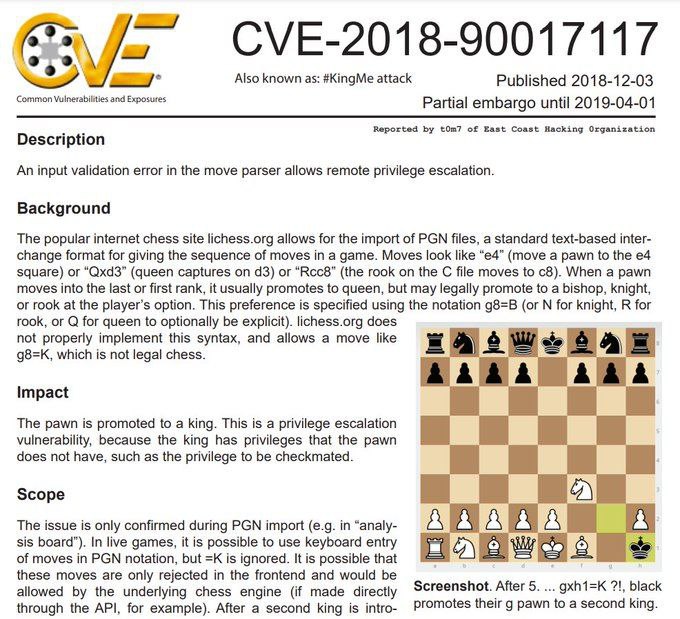
The pawn is promoted to a king. This is a privilege escalation
vulnerability, because the king has privileges that the pawn
does not have, such as the privilege to be checkmated.
Scope
The issue is only confirmed during РСМ import in “analy-
sis board”). In live games, it is possible to use keyboard entry
of moves in PGN notation, but is ignored. It is possible that
these moves are only rejected in the frontend and would be
allowed the underlying chess engine (if made directly
Screenshot. After 5. gxh1=K black
through the API, for example). After a second king is intro-
promotes their pawn to a second king.
lang: ru+en
Пользовательские термины
Свои поисковые фразы (до 280 символов). При поиске по термину счётчик растёт.
Пока нет пользовательских терминов.