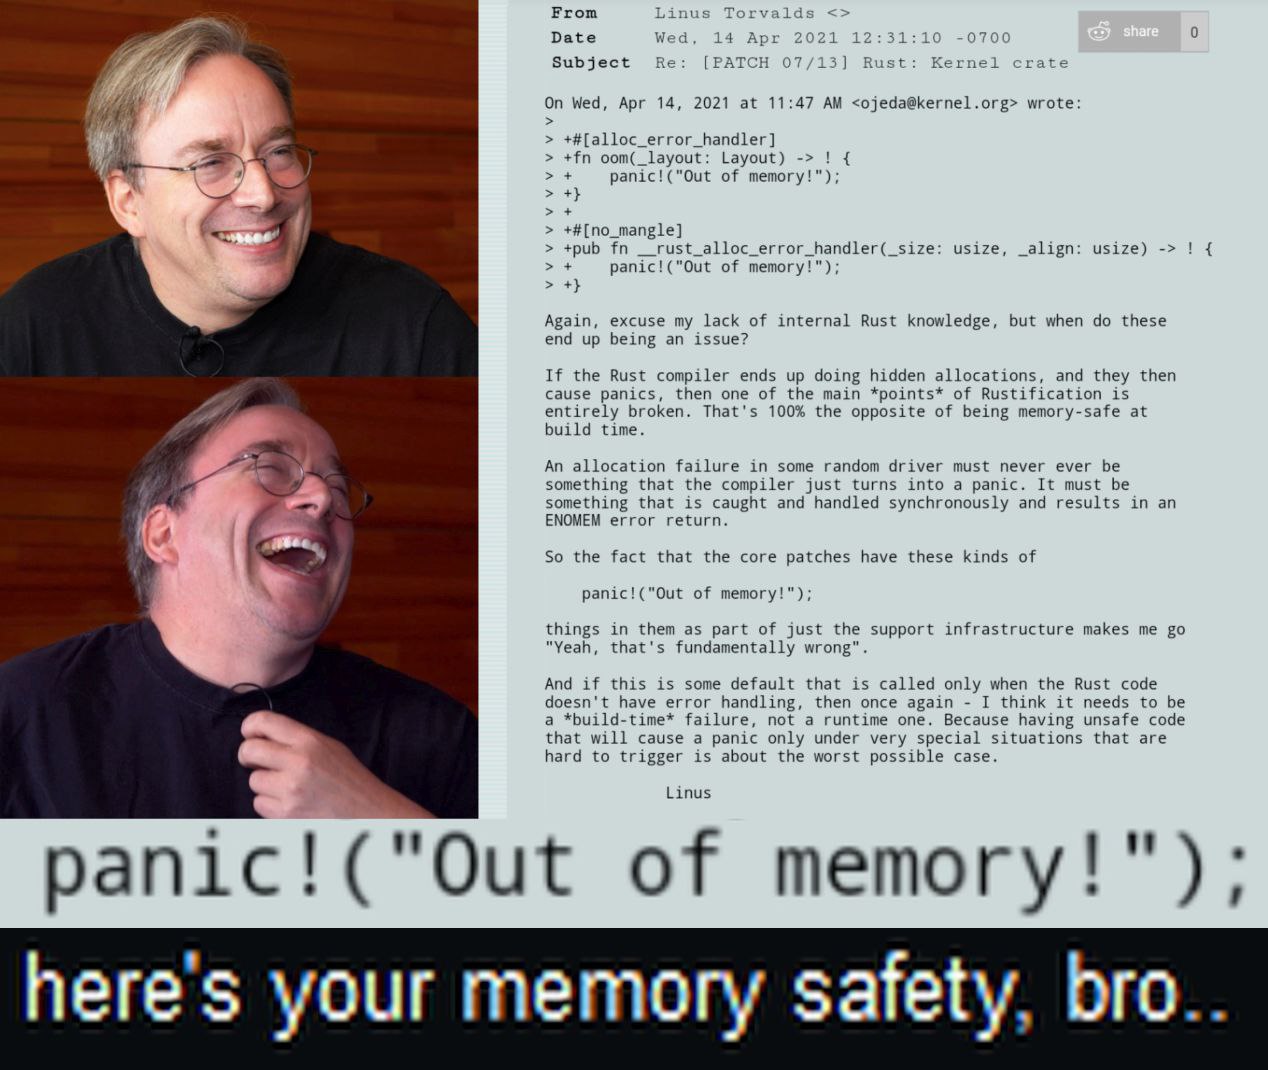
From Date 14 о Subject (PAT ernel crate On Wed, Apr 14, 2021 at 11:47 <[email protected]> wrote +#[alloc_error_handler] Layout) panic!("Out of memory!") +#[no_mangle] +pub usize, _align usize) рапс! ("
2026-09-27 02:25
telegramthe_high_council_of_frens
OCR
Текст, распознанный с картинки.
From
Date
14
о
Subject
(PAT
ernel
crate
On Wed, Apr 14, 2021 at 11:47 <[email protected]> wrote
+#[alloc_error_handler]
Layout)
panic!("Out of memory!")
+#[no_mangle]
+pub usize, _align
usize)
рапс! ("Оше of memory!");
Again, excuse my lack of internal Rust knowledge, but when these
end up being an issue?
If the Rust compiler ends up doing hidden allocations, and they then
cause panics, then one of the main *points* of Rustification is
entirely broken. That's 100% the opposite of being memory-safe at
build time.
2%
An allocation failure in some random driver must never ever be
something that the compiler
just turns into a panic.
It must be
something that is caught and handled synchronously and results in an
ENOMEM error
return.
So the fact that the core patches have these kinds of
of memory!");
things in them as part of just the support infrastructure makes me
"Yeah, that's fundamentally wrong".
And if this is some default that is called only when the Rust code
doesn't have error handling, then once again I think it needs to be
a *build-time* failure, not a runtime one. Because having unsafe code
that will cause a panic only under very special situations that are
hard to trigger is about the worst possible case.
Linus
‘Out of memory!"
ere’s your memory safety, bro..
lang: ru+en
Пользовательские термины
Свои поисковые фразы (до 280 символов). При поиске по термину счётчик растёт.
Пока нет пользовательских терминов.